Comply · Governance & risk
GRC
Governance, Risk & Compliance
Audit-ready, accredited and in control.
GRC is the governance layer — policy and obligations, risk and framework readiness (including ISO/IEC 42001 for AI management), business-continuity and disaster-recovery plans, identity and right-to-work clearance, and the accredited deployment posture that regulated and government work demands.
Modules in this suite
- Compliance
Policy, obligations, risk and framework readiness — ISO/IEC 42001, BCP/DR continuity and access certification.
- IRAP
Accredited, assessed deployment posture.
- Clearance
Identity, right-to-work and credential verification.
A look inside
GRC, in the product.
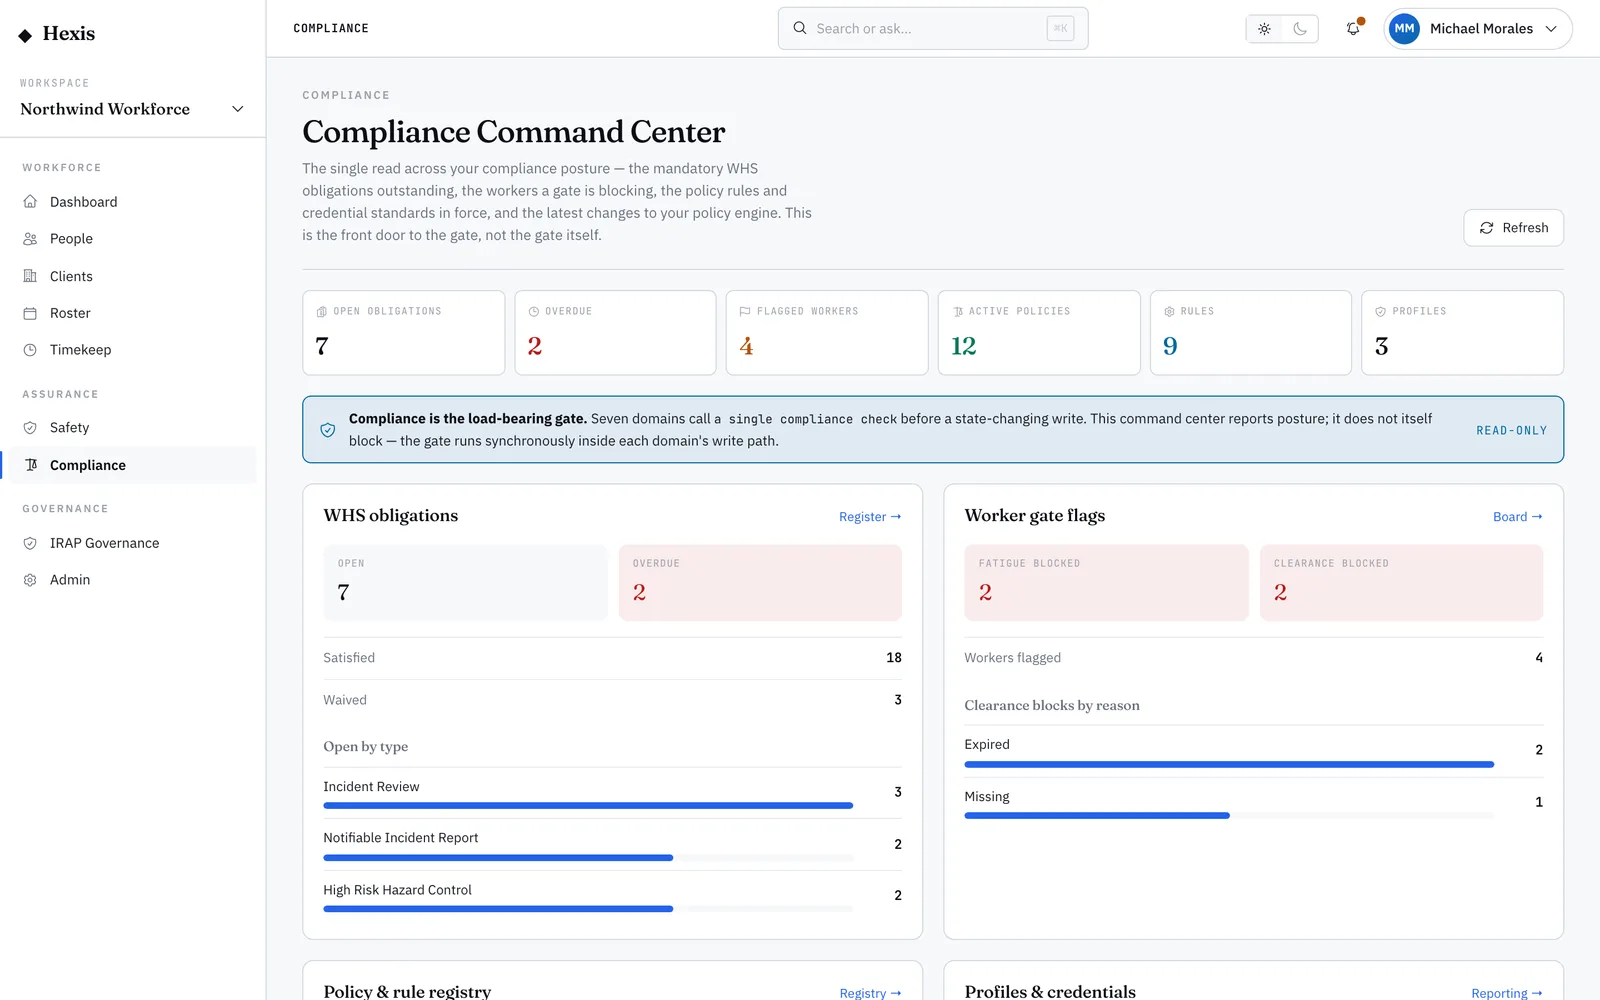
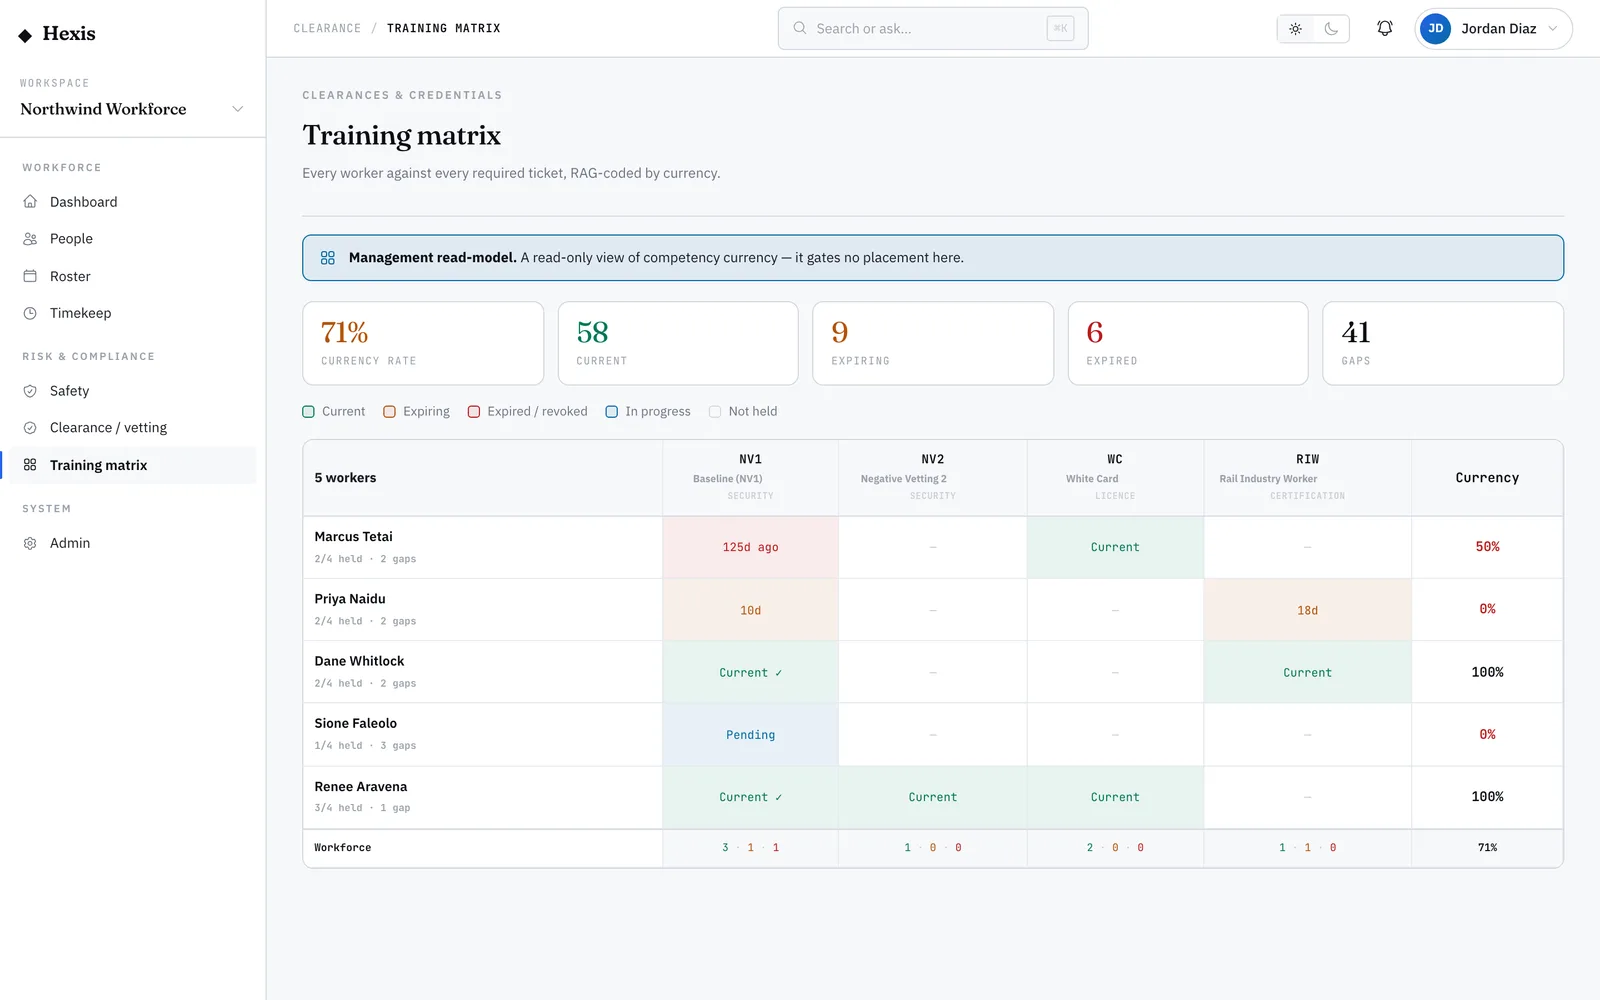
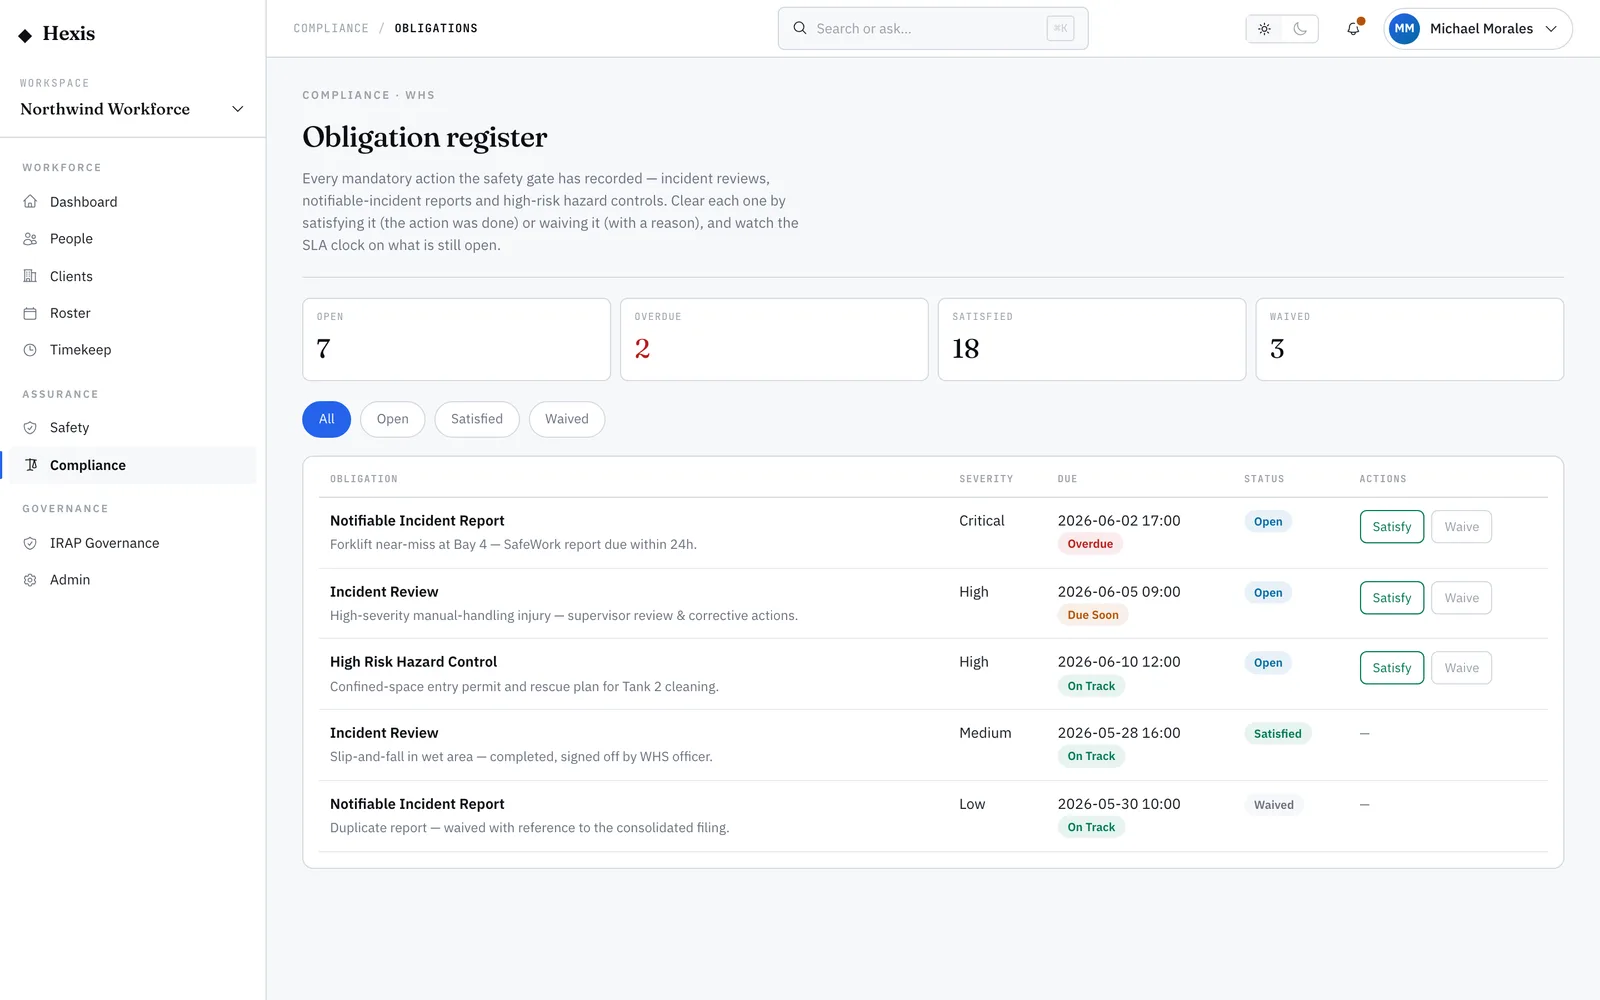
The actual governance, risk & compliance screens — the same surfaces your team works in every day, shown with sample data.
Guided walkthrough
Take the narrated GRC tour
8 screens · ~3 min · no sign-up
What it is
The comply stage, run end to end.
GRC is the governance layer that runs across everything. It holds the obligations and policy that gate the work, the risk and framework readiness that proves you’re on top of them, the identity and right-to-work clearances that gate who can do the work, and the accredited deployment posture that regulated and government work demands.
Compliance is the load-bearing gate — a single check runs before state-changing writes in the domains that need it, so the rules are enforced in the flow of work rather than audited after the fact. Framework readiness tracks you against the standards that matter — including ISO/IEC 42001, the AI-management-system standard — while access certification and segregation-of-duties reviews keep entitlements right and conflicts caught.
Governance also means being ready for the bad day: business-continuity and disaster-recovery plans, with continuity tests and drills that prove they work, sit alongside the clearance register and training matrix. And for regulated and public-sector work, Hexis runs in an accredited, IRAP-assessed posture from the same codebase — so the controls that satisfy an assessor are the controls that protect your data every day.
Rules in the flow, not after
Obligations and policy are checked as work happens — enforced, with audit-ready evidence.
Ready for the standard — and the audit
Framework readiness (including ISO/IEC 42001), access certification and segregation of duties, with the evidence assembled as you go.
Accredited when it counts
An IRAP-assessed deployment posture for regulated and government work, with continuity and DR plans tested before you need them.
Capabilities
Everything GRC does.
75 data objects · 171 typed actions — drawn from the Hexis capability model.
- Obligations and policy with audit-ready evidence
- A single compliance check before state-changing writes
- Framework readiness — ISO/IEC 42001 and more
- Business-continuity and DR plans, with continuity tests
- Access certification and segregation of duties
- Identity, right-to-work and clearance register
- Risk, issue and exception registers
- Accredited (IRAP-assessed) deployment posture
Guided workflows
- Renew an expiring clearance
validity extended, no break in eligibility, worker stays cleared to work.
Typed actions
Where it sits
Part of the Comply stage.
GRC anchors the comply stage of the workforce lifecycle, working on the same shared worker record as every other suite.
Intelligence, woven in
A capable assistant — never on its own.
GRC does its job whether or not anyone asks it to think. Where it helps, it helps quietly — and a person stays on the call that matters.
Clearance reads and checks identity and credential documents on upload, flagging mismatches and expiries before they become a problem.
A supporting capability — reviewable, audited, and always with a person on the call that matters.
Add GRC to your platform.
GRC ships in a tier or can be added à-la-carte to any plan. Tell us your headcount and we'll price it for your workforce.