Comply · Governance & risk
Governance, Risk & Compliance
GRC is the governance layer — policy and obligations, risk and framework readiness (including ISO/IEC 42001 for AI management), business-continuity and disaster-recovery plans, identity and right-to-work clearance, and the accredited deployment posture that regulated and government work demands.
Clearances
5 guidesVerify a worker document
Check a worker’s identity, right-to-work or credential document against the record and capture the verification in one pass.
Work the clearance register
Scan, filter and triage every worker clearance across the workforce from one searchable table.
Read the clearance matrix
See your whole workforce against every required ticket in one grid — current, expiring, lapsed, in progress or not held.
Set up clearance types
Define what credentials exist in your organisation — name, category, validity period and whether they need verification.
Manage medical clearances
Track fitness-for-work medicals across the workforce and stop deployment when a medical lapses or a worker is found unfit.
Expiry & renewals
1 guideObligations & policy
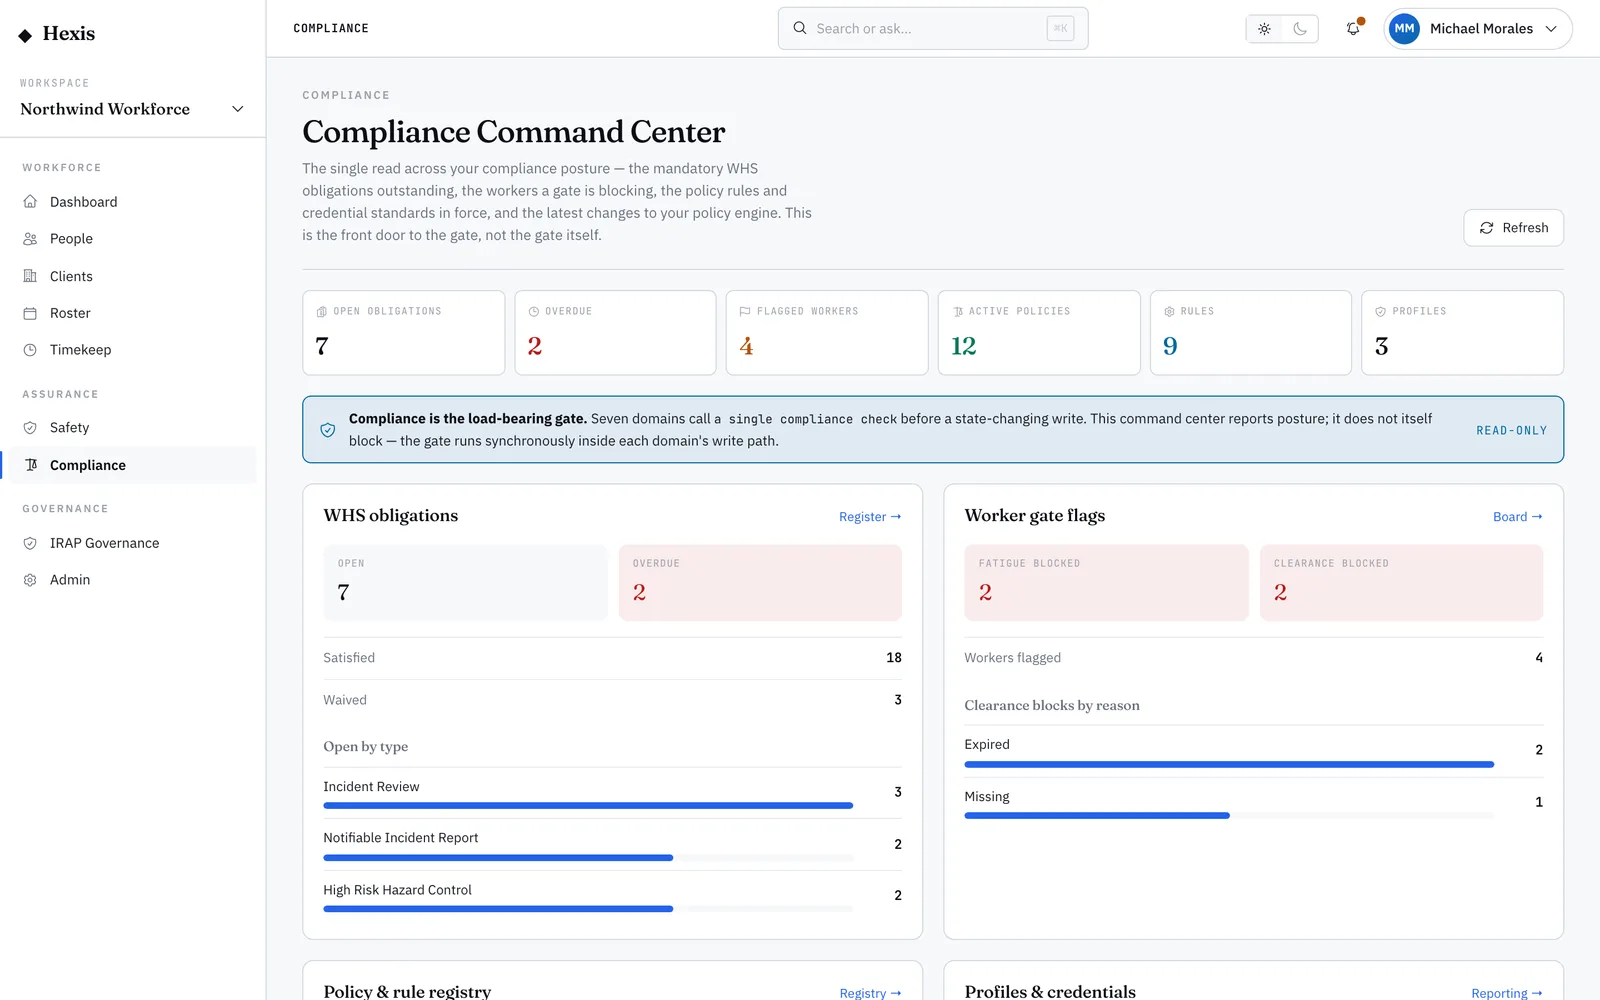
2 guidesClear the obligations register
Track every mandatory safety action with its deadline, and close each one by marking it satisfied or waiving it with a reason.
Browse policies and rules
See every enforceable policy in your organisation, which industry profile it belongs to, and whether it actively blocks or just documents an expectation.
Attestations & audit
2 guidesRun policy attestations
Track who has acknowledged each policy, chase the outstanding sign-offs, and record your own acknowledgements.
Run an internal audit
Run audit engagements, track findings to remediation, and keep control tests current from one internal-audit surface.